Trust
Control can be reviewed.
Permissions, encryption and verifiable records to review who accesses video and what they do with it. Controls and their limits are agreed with your team.
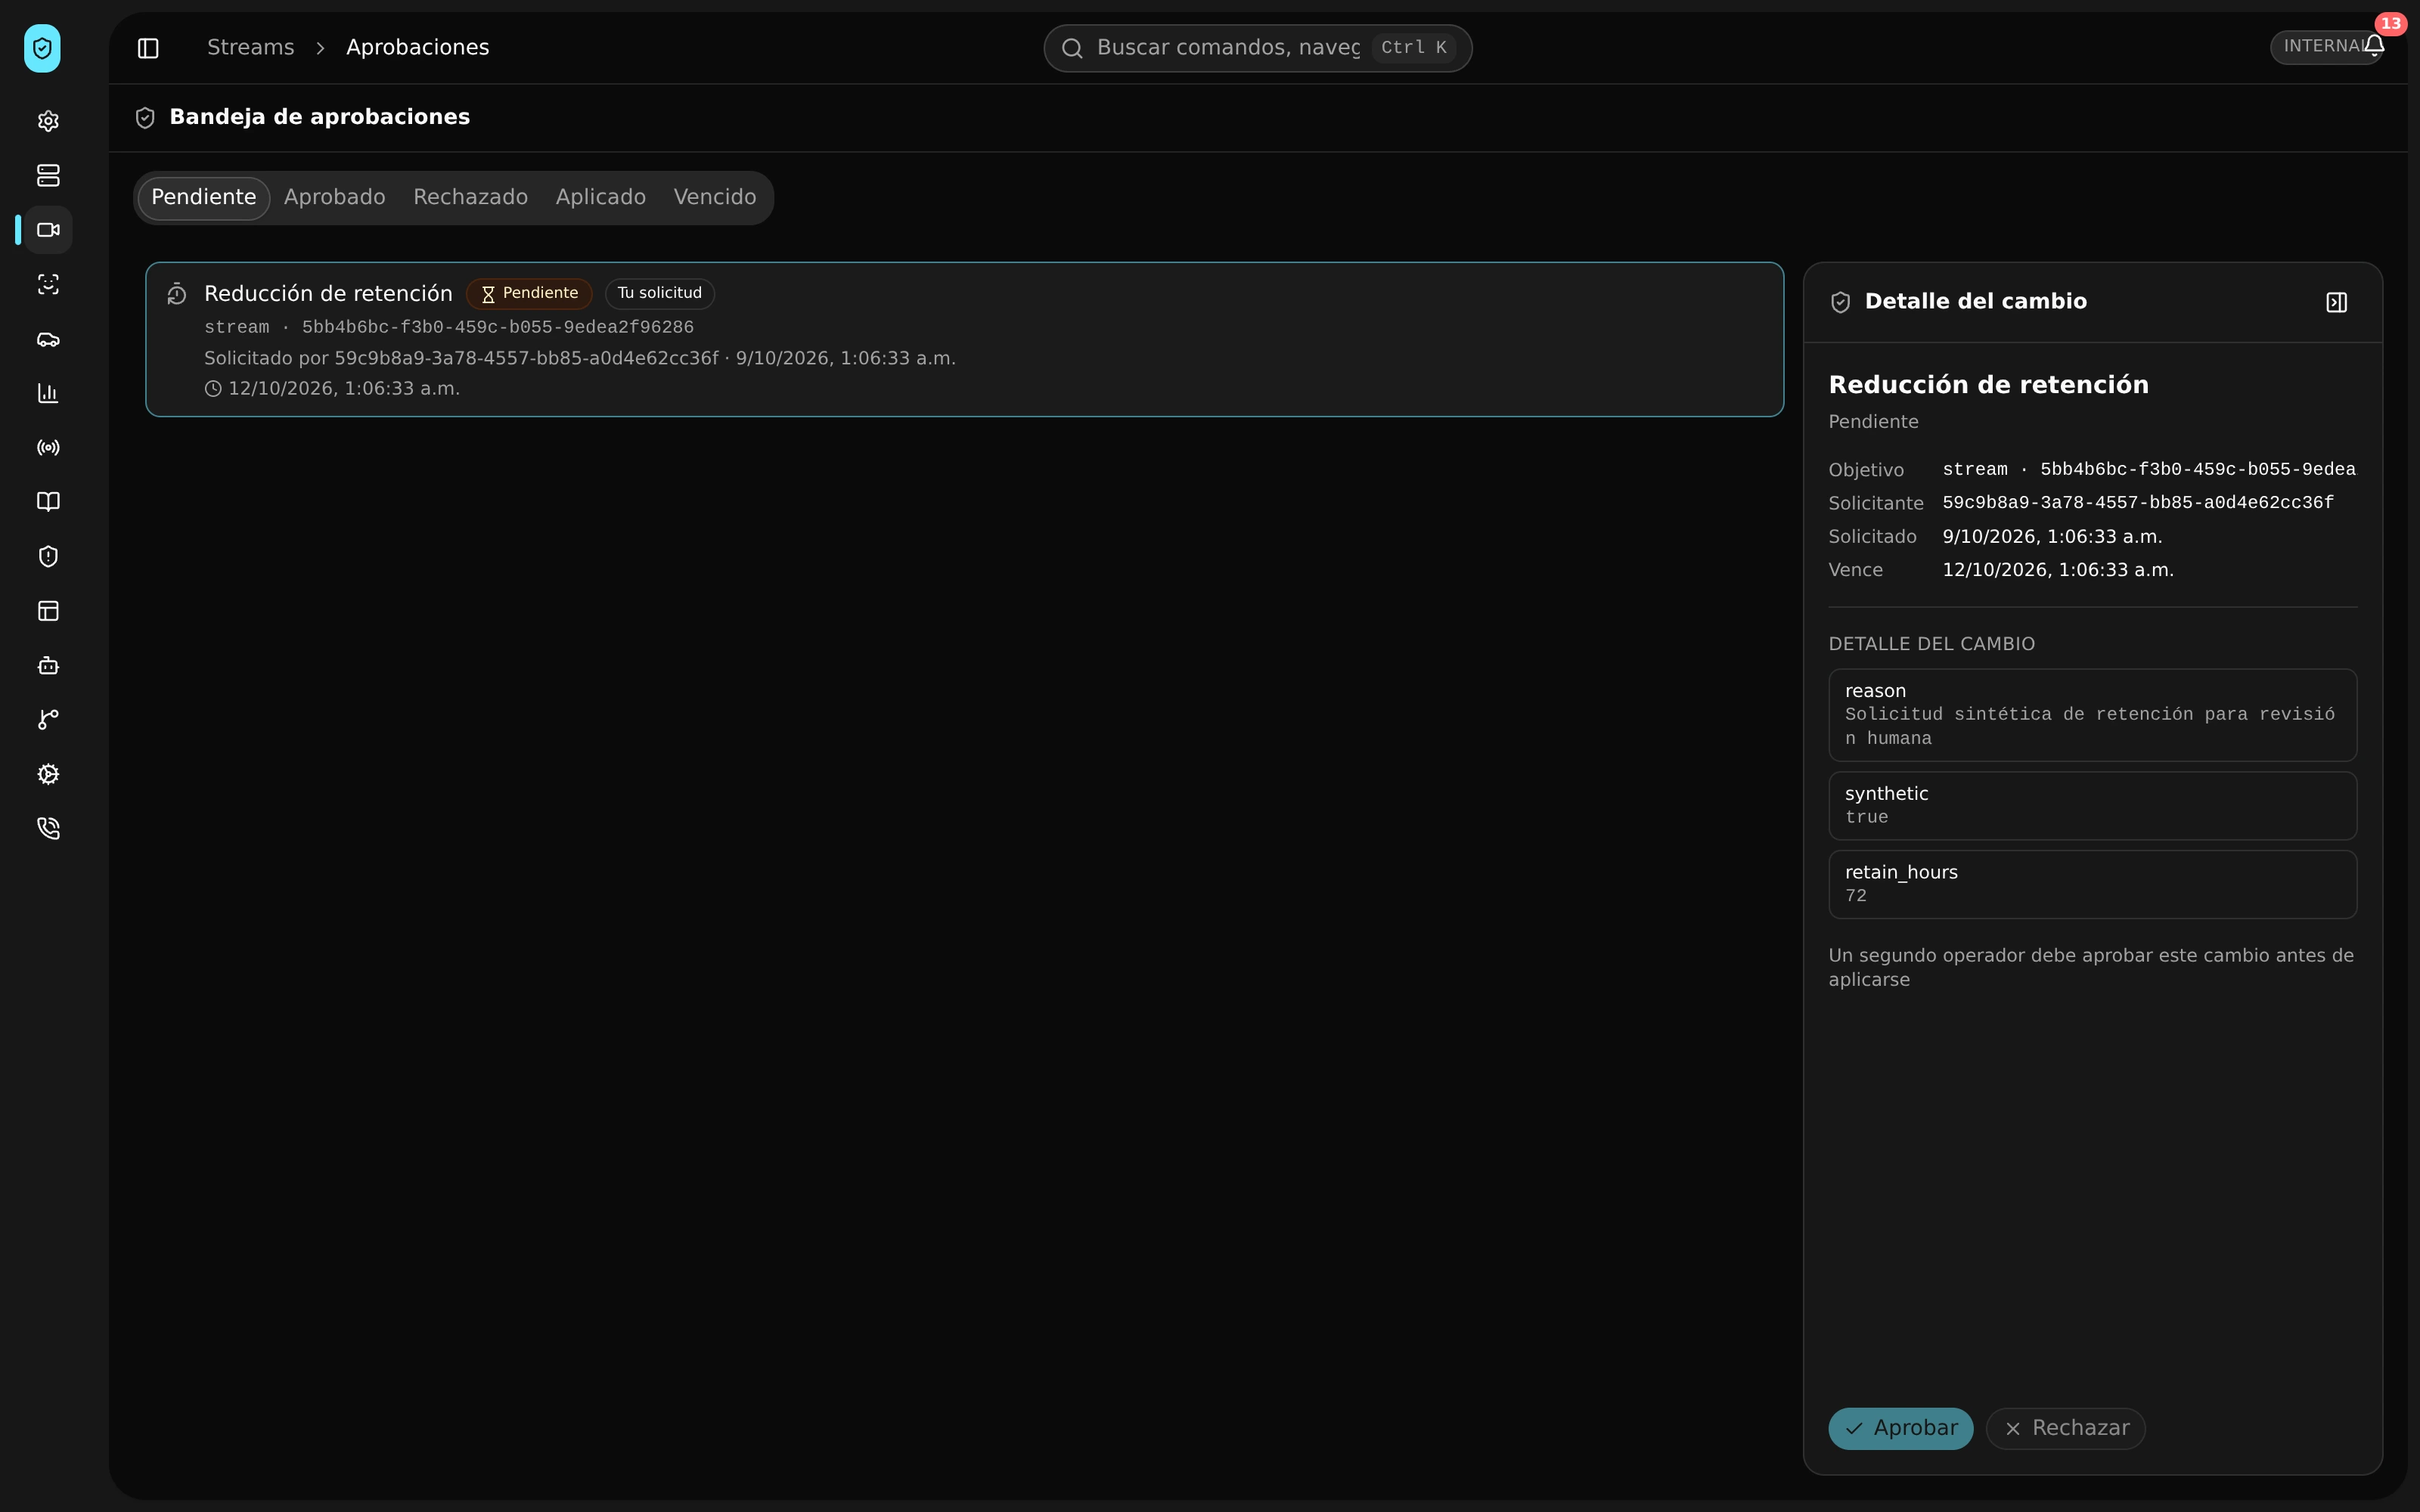
Production · Product capture with demonstration data.
From account to archive
Five control families.
Review available capabilities with your technical team. Corporate connections are validated against your systems and policies.
Identity and access
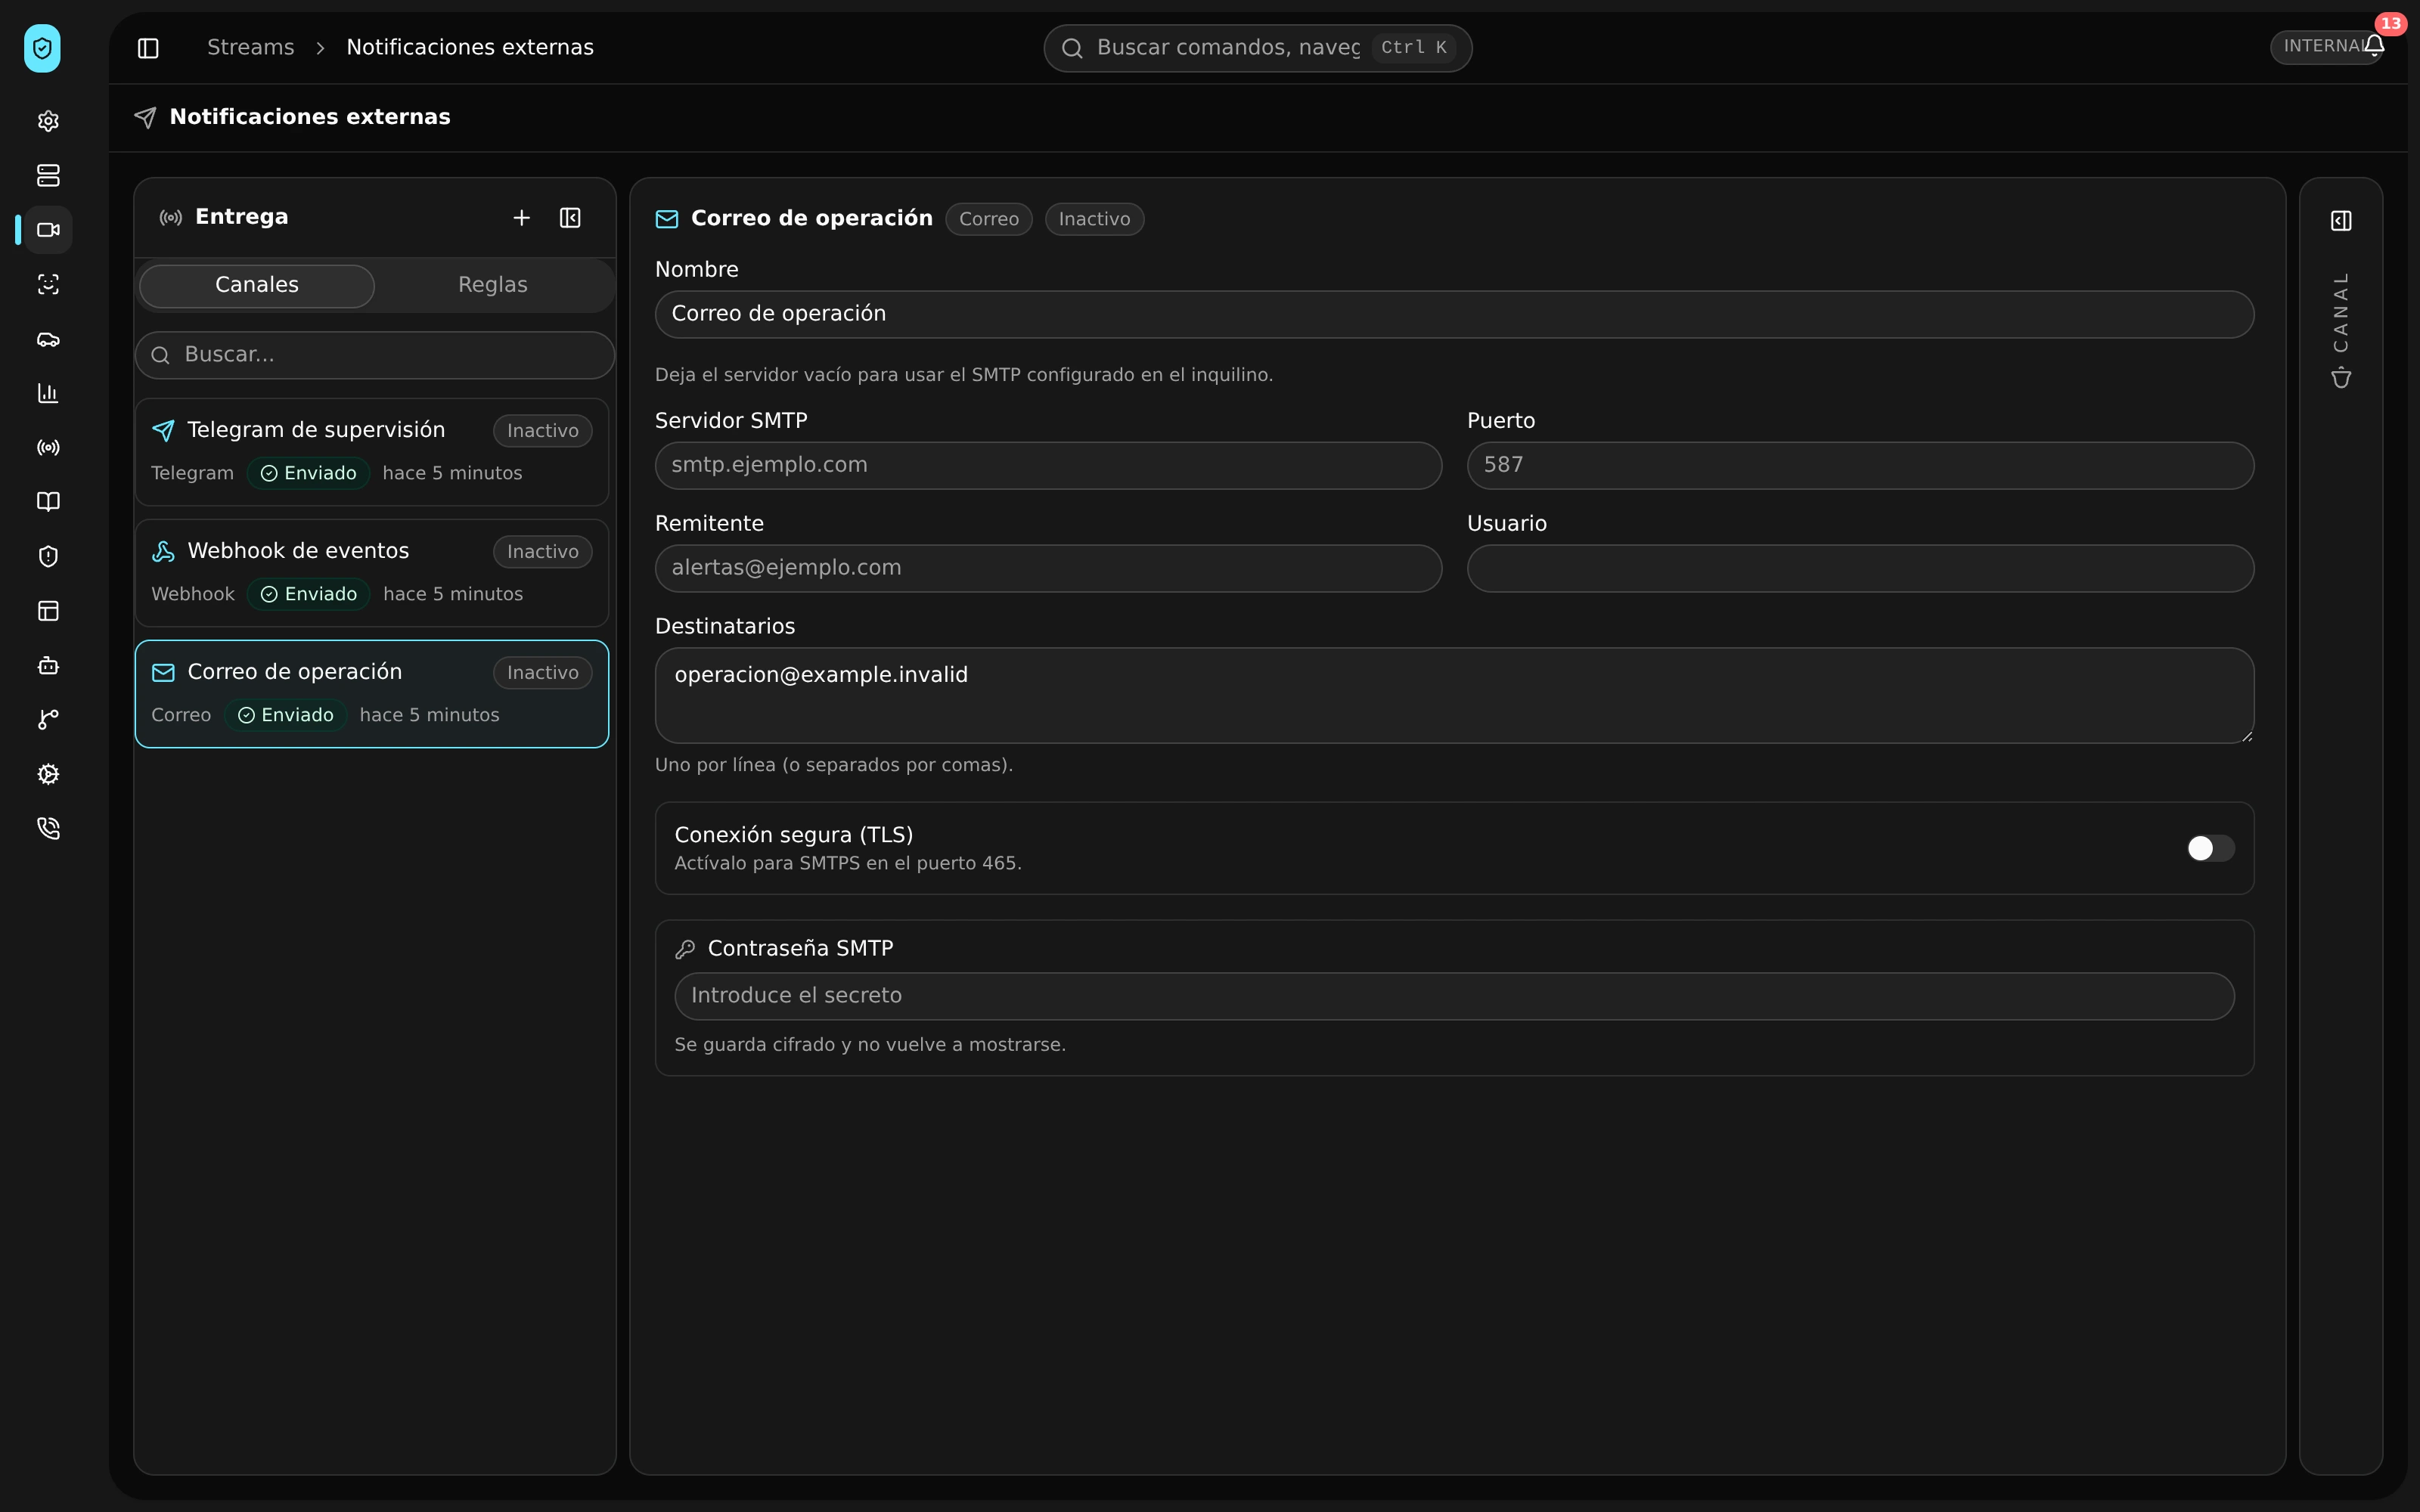
Production · Product capture with demonstration data.
Camera roles
Assign permissions by user role and camera responsibility.
Stronger sign in
Protect accounts with an additional authentication factor and configurable access policies.
Inactive account expiry
Remove access from inactive accounts according to the agreed policy.
Network access restriction
Limit platform access to authorized networks.
Corporate identity
Connects to your directory and identity provider to manage access.
Service credentials
Control and revoke access for systems connected to the platform.
Encryption and isolation
Access is scoped by organization. Central storage and communications have their own controls; local scope is verified at the site.
Central media encryption
Protect clips and evidence in central storage with managed keys.
Protected communications
Protect web access and data exchange with the platform.
Audit and evidence
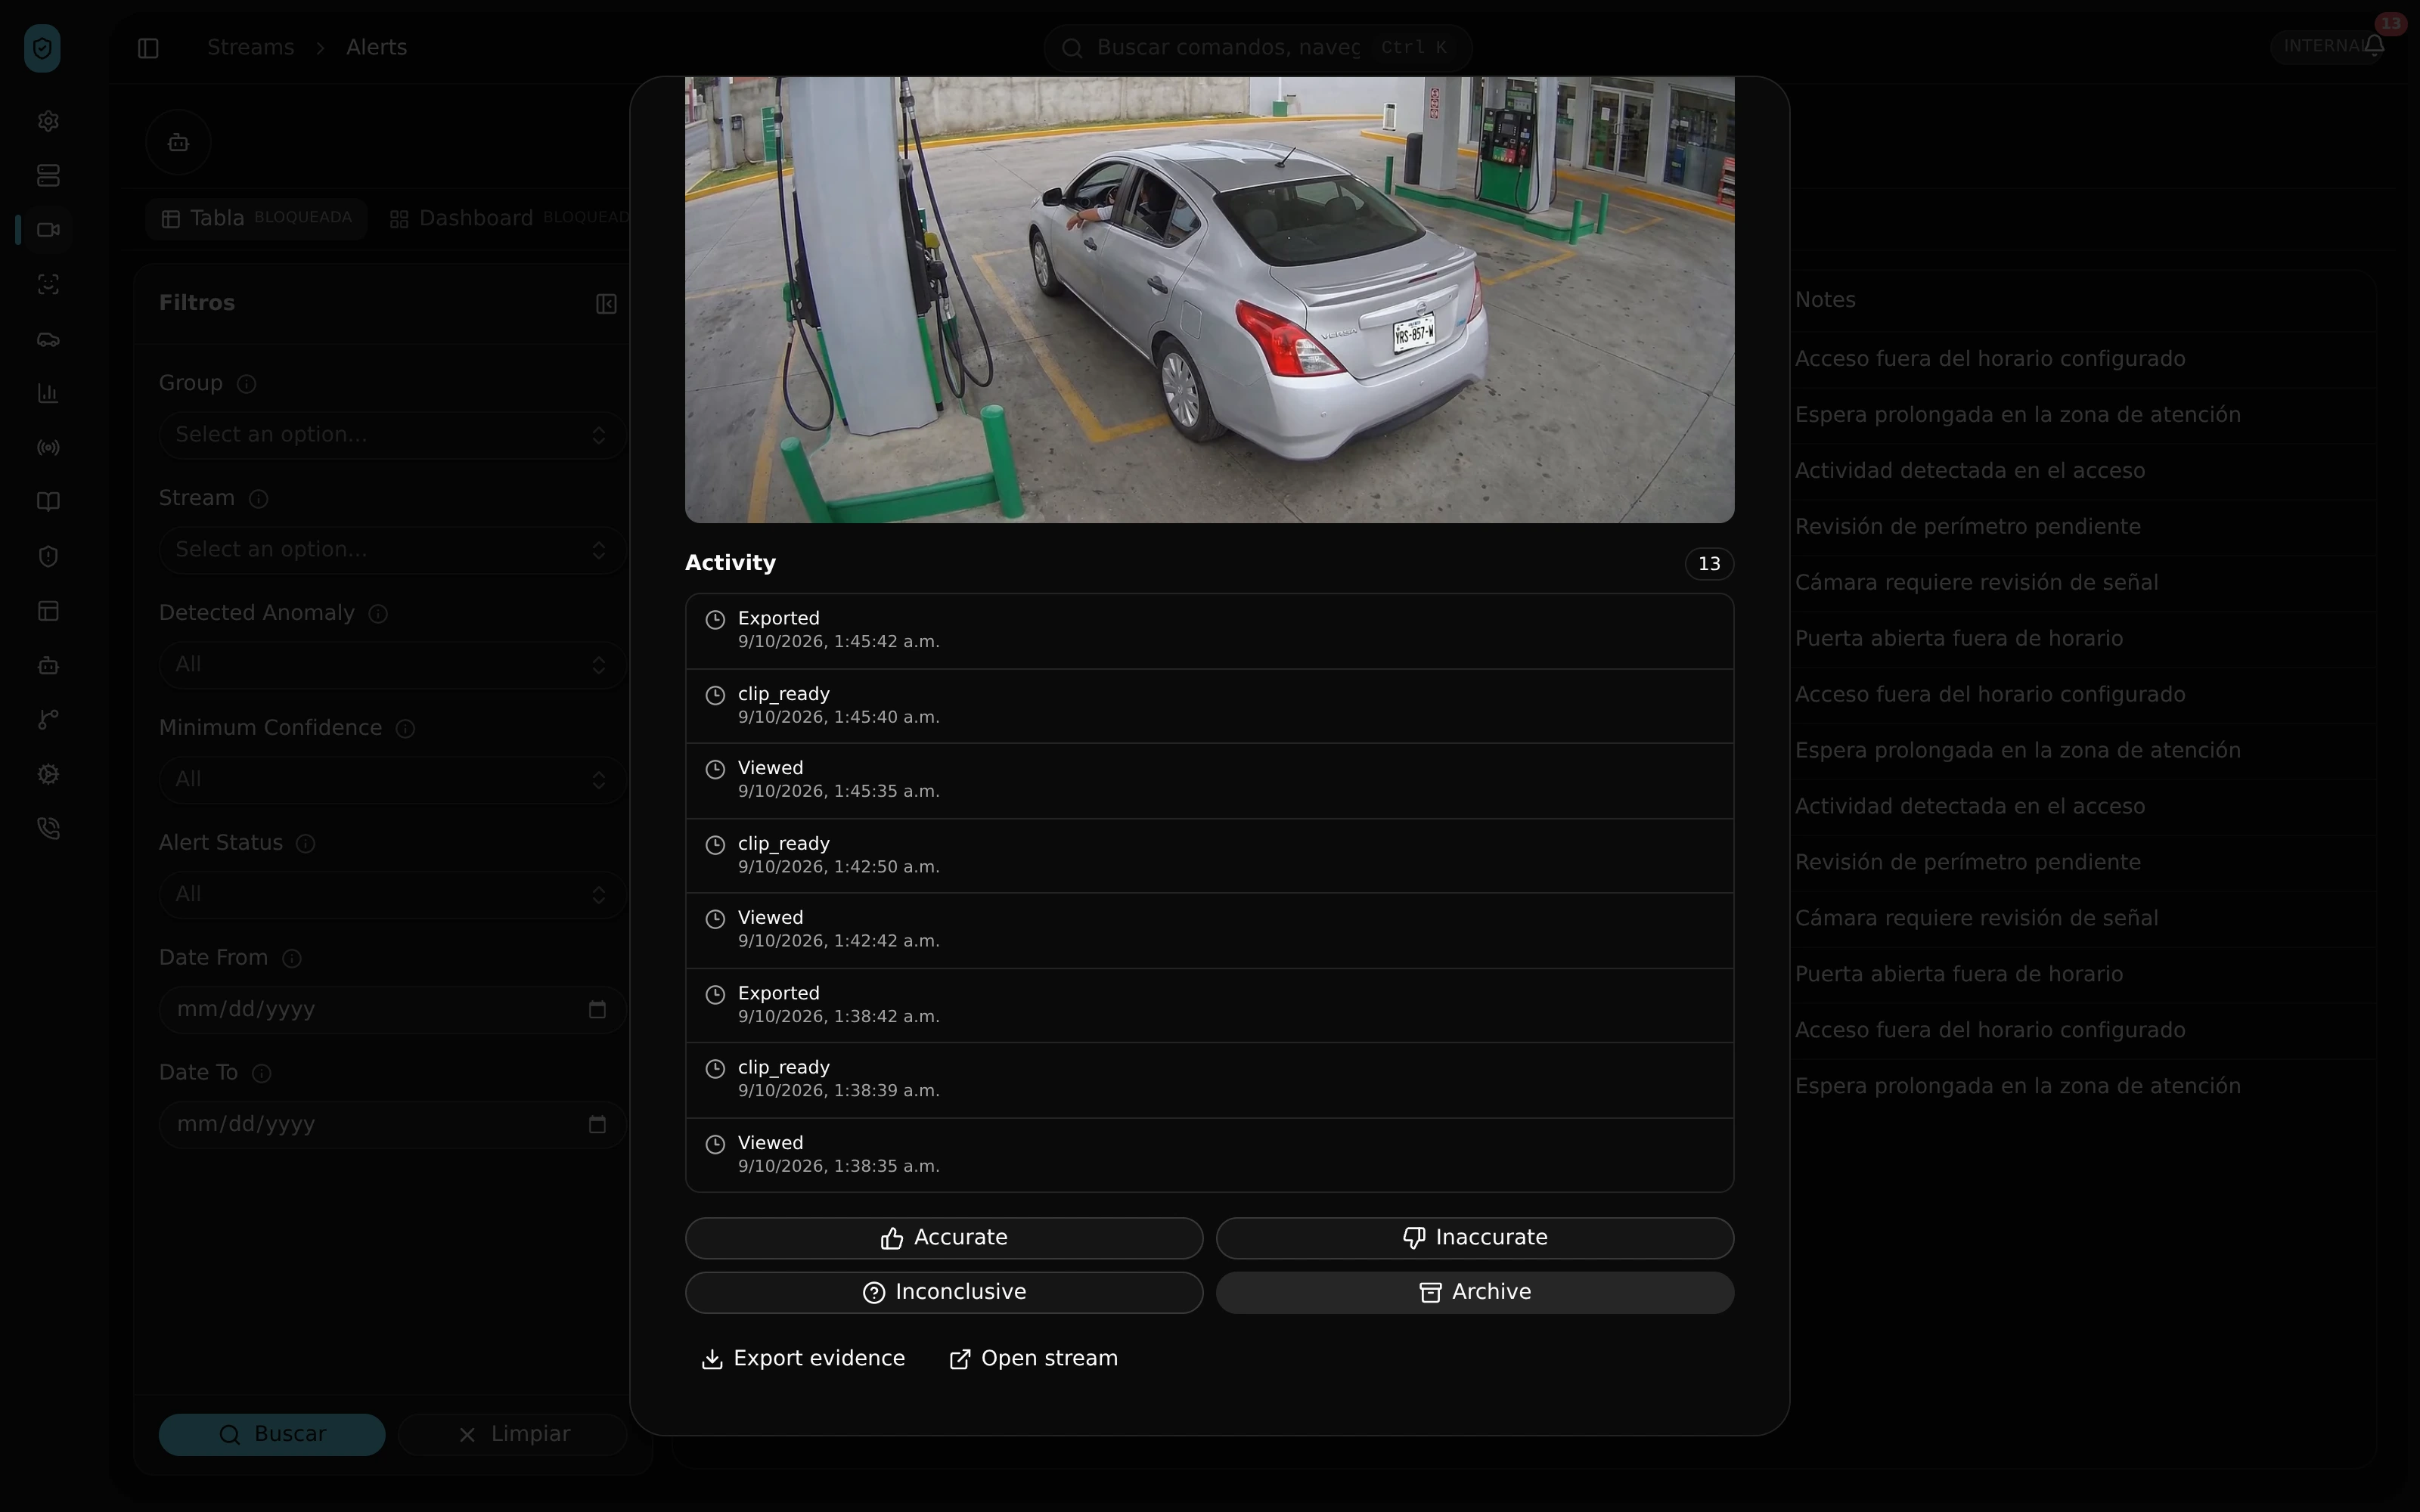
Production · Product capture with demonstration data.
Verifiable audit
Review actions and exports through a record that enables tamper detection.
Operator activity
Review who used views and exported information to oversee operations.
Dual authorization
Require independent review for sensitive operations covered by policy.
Controls and evidence
Prepare security reviews with documented controls and exportable evidence.
Backup and continuity
Critical information backups are verified through restoration. Video backup, an alternate recorder and a contingency site remain on the roadmap, pending validation.
Backup and restore
Recover critical information using backups with restore verification.
Central resilience
Support central operations with redundant services and tested recovery.
Service recovery
Recover stopped connections and processes through automatic supervision.
Controlled updates
Apply changes using a procedure with checks and a rollback option.
Privacy
Data rights management
Organize ARCO rights requests with available controls; the procedure and responsibilities under Mexico’s LFPDPPP are reviewed for each project.
Privacy masks
Hide sensitive areas in live viewing and analysis.
Export redaction
Reduce exposure of people when sharing a blurred clip.
Visible limits
Declared gaps
These evaluations have not been completed. Review what we do today and what remains before deciding.
- CERT-01
No SOC 2 / ISO 27001 certification yet
- ENV-01
Hypervisors: not evaluated
Declared scope status. This is not a certification or an external assessment.
- Documented controls
- We review controls and evidence with your security team. A project review does not constitute external certification.
- Security reviews
- Vulnerability reviews and verifiable records help prioritize fixes and examine actions.
- Environment validation
- Hardware, connections and recovery are tested within the agreed scope before accepting the deployment.
Before expanding
Review is part of the pilot too.
- Clear owners
- We agree on who manages access, keys and data requests.
- Reviewable evidence
- Acceptance criteria identify the controls your team needs to verify.
- Written limits
- The proposal distinguishes available controls, connections and pending functions.
The next step
Put the controls on the table.
Share your security team’s requirements to define which evidence to review in the pilot.